Trust at Runtime: Rethinking Identity, Access, and Control for Agentic AI
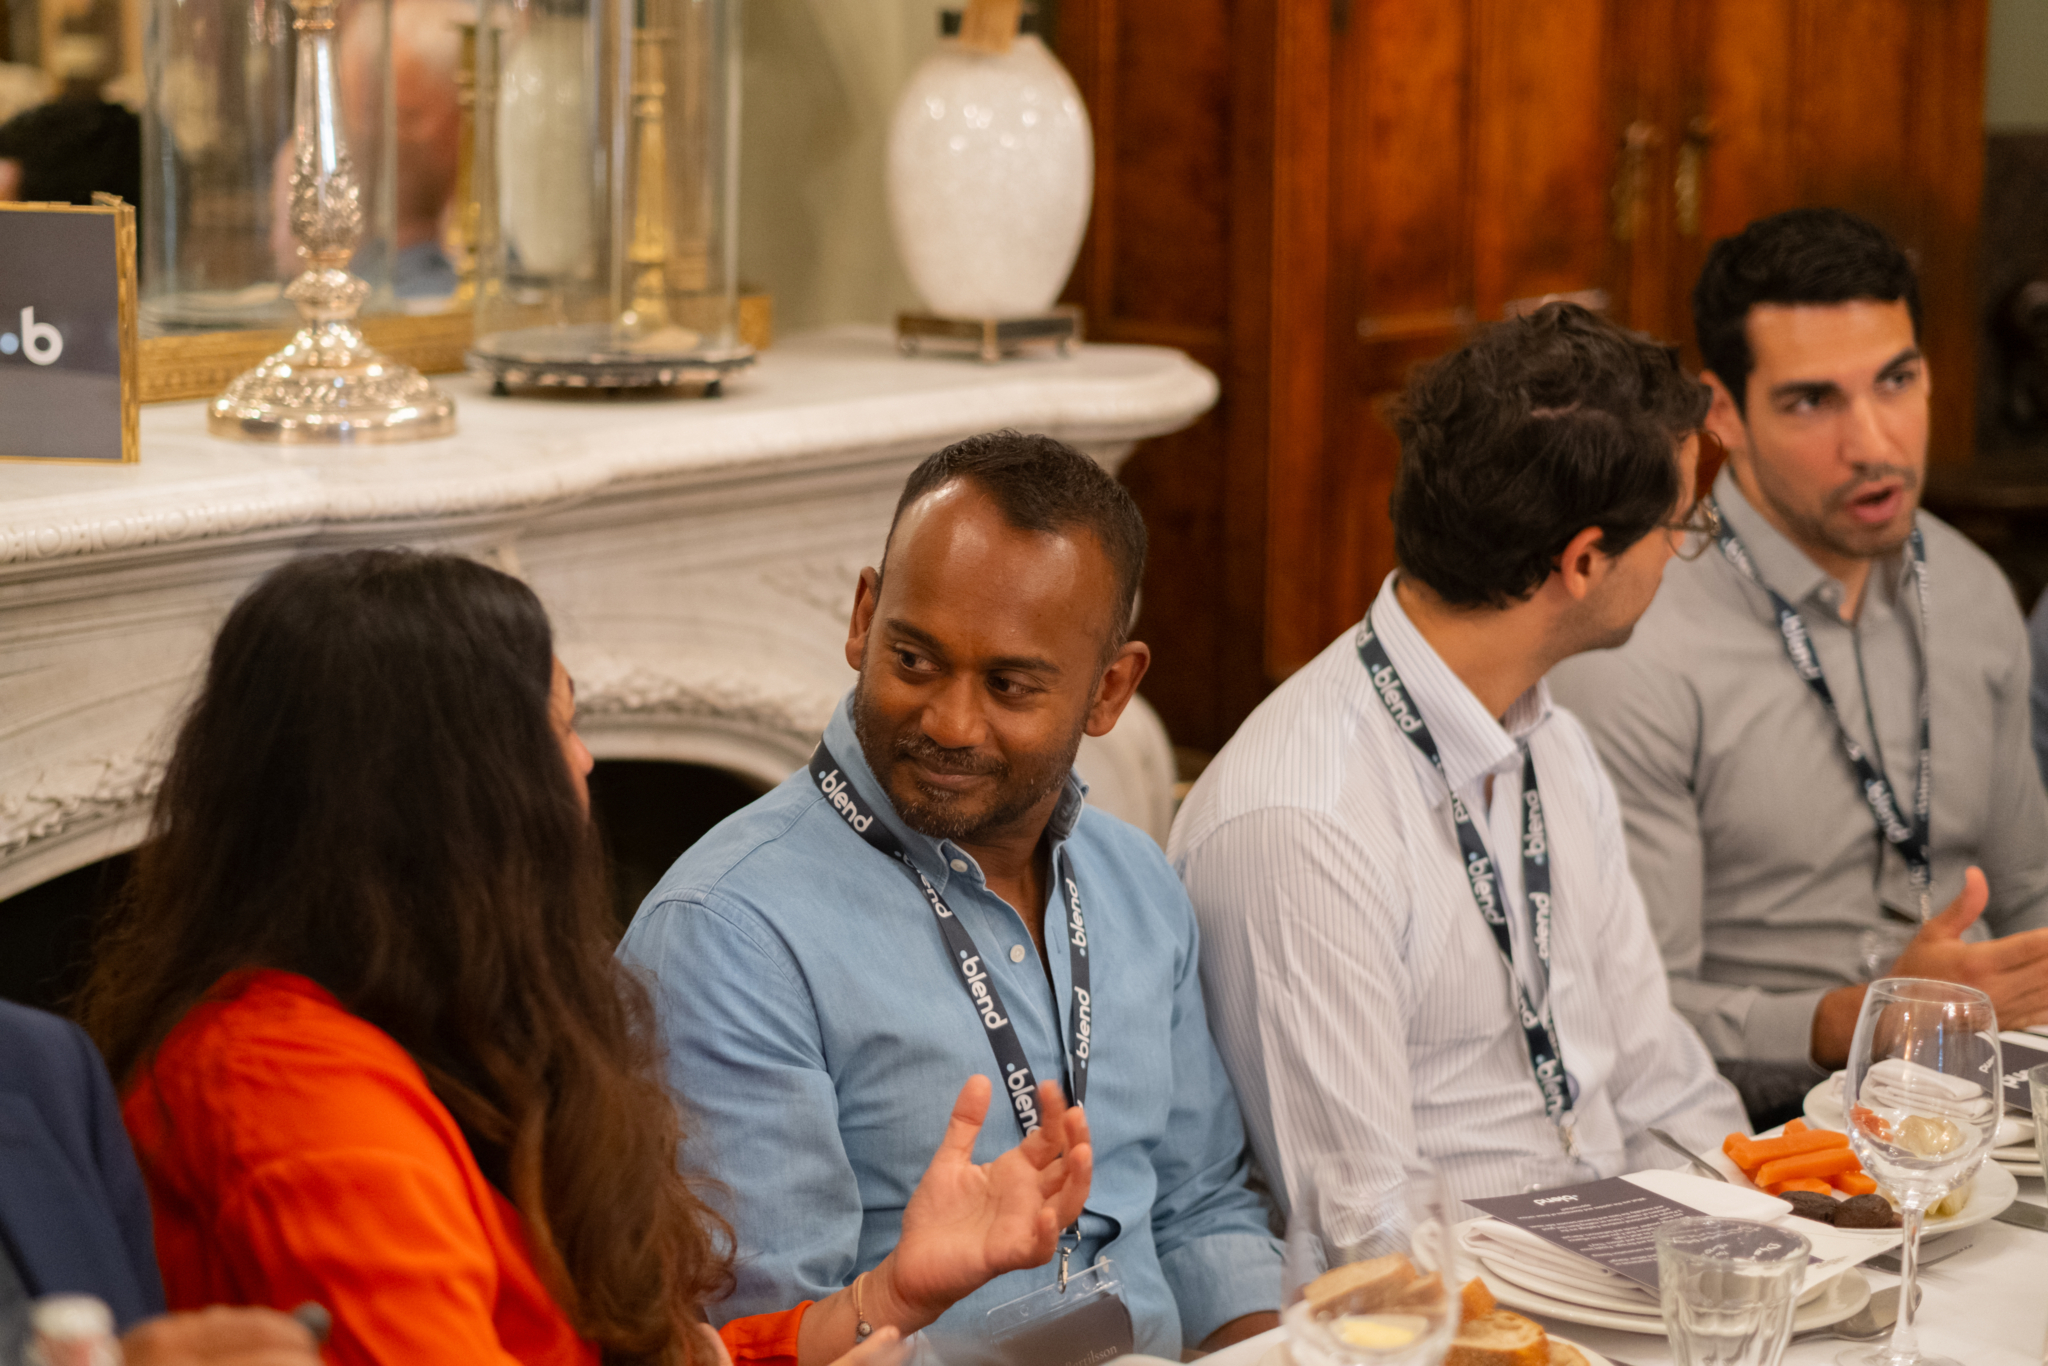
Join Blend and HashiCorp, an IBM Company, for an executive dinner exploring how enterprises can rethink identity, access and zero trust for agentic AI. Discover how leaders can govern non-human identities, enforce trust at runtime and scale autonomous systems without sacrificing visibility, accountability or control.
Agentic AI is fundamentally changing the relationship between identity, access, and enterprise security. Traditional identity models were designed around relatively predictable assumptions: a human authenticates, receives access, and operates within defined permissions. AI agents don’t necessarily behave that way. They can operate continuously, call new tools, assume roles, request credentials, and take actions across systems on behalf of people and other machines.
As organizations move agentic AI from experimentation into production, that creates an entirely new control challenge. Static permissions and periodic access reviews may no longer be enough when autonomous systems make decisions and request access in real time. Leaders need to know not only what an agent did, but whose authority it acted under, why the action was permitted, and whether that authority was still appropriate at the precise moment of execution. HashiCorp identifies this shift from static compliance toward dynamic, runtime-enforced controls as one of the defining security requirements of agentic AI.
Join Blend and HashiCorp, an IBM Company, for an executive dinner exploring how identity, zero trust, and security must evolve for an agentic enterprise. Through candid peer discussion, we’ll examine how organizations can govern non-human identities, establish appropriate boundaries for autonomous systems, preserve the connection between human intent and agent action, and scale AI without sacrificing visibility, accountability, or control.
When Identity Stops Being Human How traditional identity and access models need to evolve as autonomous AI agents increasingly act on behalf of people, applications and other machines.
From Standing Access to Runtime Trust The shift from static permissions toward dynamic, real-time authorization, and how enterprises can determine what an AI agent should be allowed to do at the precise moment it acts.
Preserving Human Intent & Accountability How organizations can trace autonomous actions back to their original human intent, maintaining visibility into who authorized an action, which permissions were used and why it was allowed.
Zero Trust for the Agentic Enterprise Does agentic AI require a fundamental rethink of zero trust, and how leaders can balance autonomy, least privilege and strong security guardrails without slowing innovation.
Event agenda
01
Cocktails & networking
6:00 – 6:30 PM
02
Opening remarks & panel discussion
6:30 – 7:15 PM
03
Dinner & guided discussion
7:15 – 8:45
04
Event wrap-up & group reflection
8:45 – 9:00PM
Why should you attend?
Understand where traditional identity and access approaches may fall short as autonomous agents move from experimentation into production.
Explore practical considerations for managing AI agents that operate continuously, assume roles, request credentials and interact across multiple enterprise systems.
Discuss how runtime authorization, least privilege and zero-trust principles can enable useful agent autonomy while limiting risk and potential blast radius.
Exchange perspectives with C-suite executives and senior technology leaders responsible for AI infrastructure, security, cloud, identity and enterprise architecture.
Who should attend
This discussion is designed for C-suite executives and senior technical decision-makers responsible for AI infrastructure, security, cloud, identity, and enterprise architecture.
Venue
Table 13
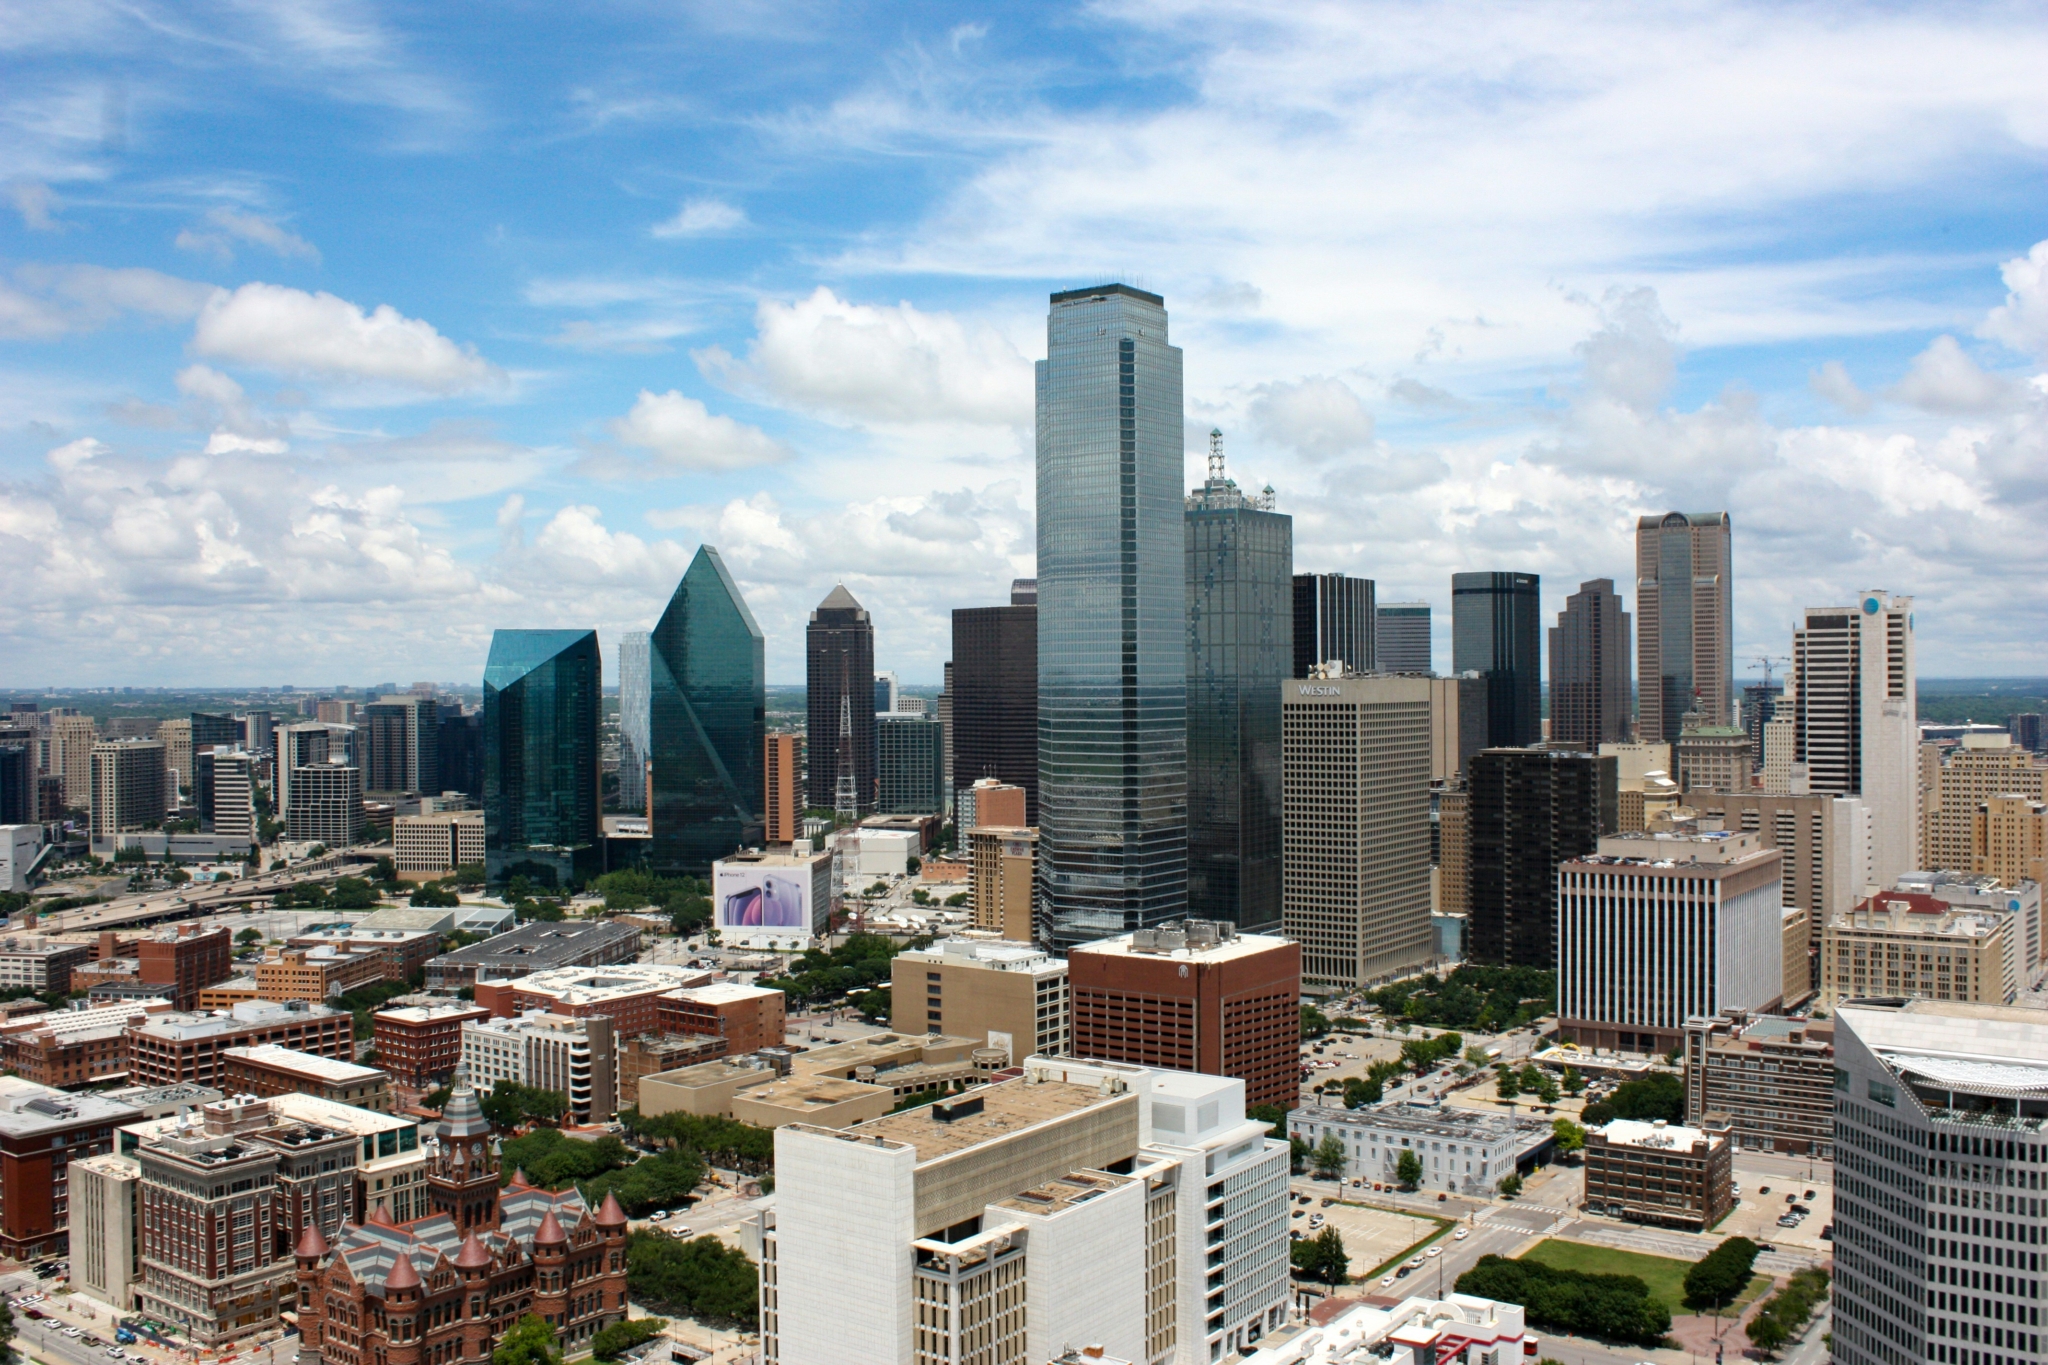
4812 Belt Line Rd Dallas Texas 75254 United States
Evolving From Technology Provider to Strategic Partner
Join Blend and Comcast Business for an exclusive executive dinner exploring how technology solution providers can evolve beyond connectivity to become trusted strategic partners. Discuss changing customer expectations, opportunities across networking, cybersecurity and managed services, and strategies for building long-term customer value and sustainable growth.